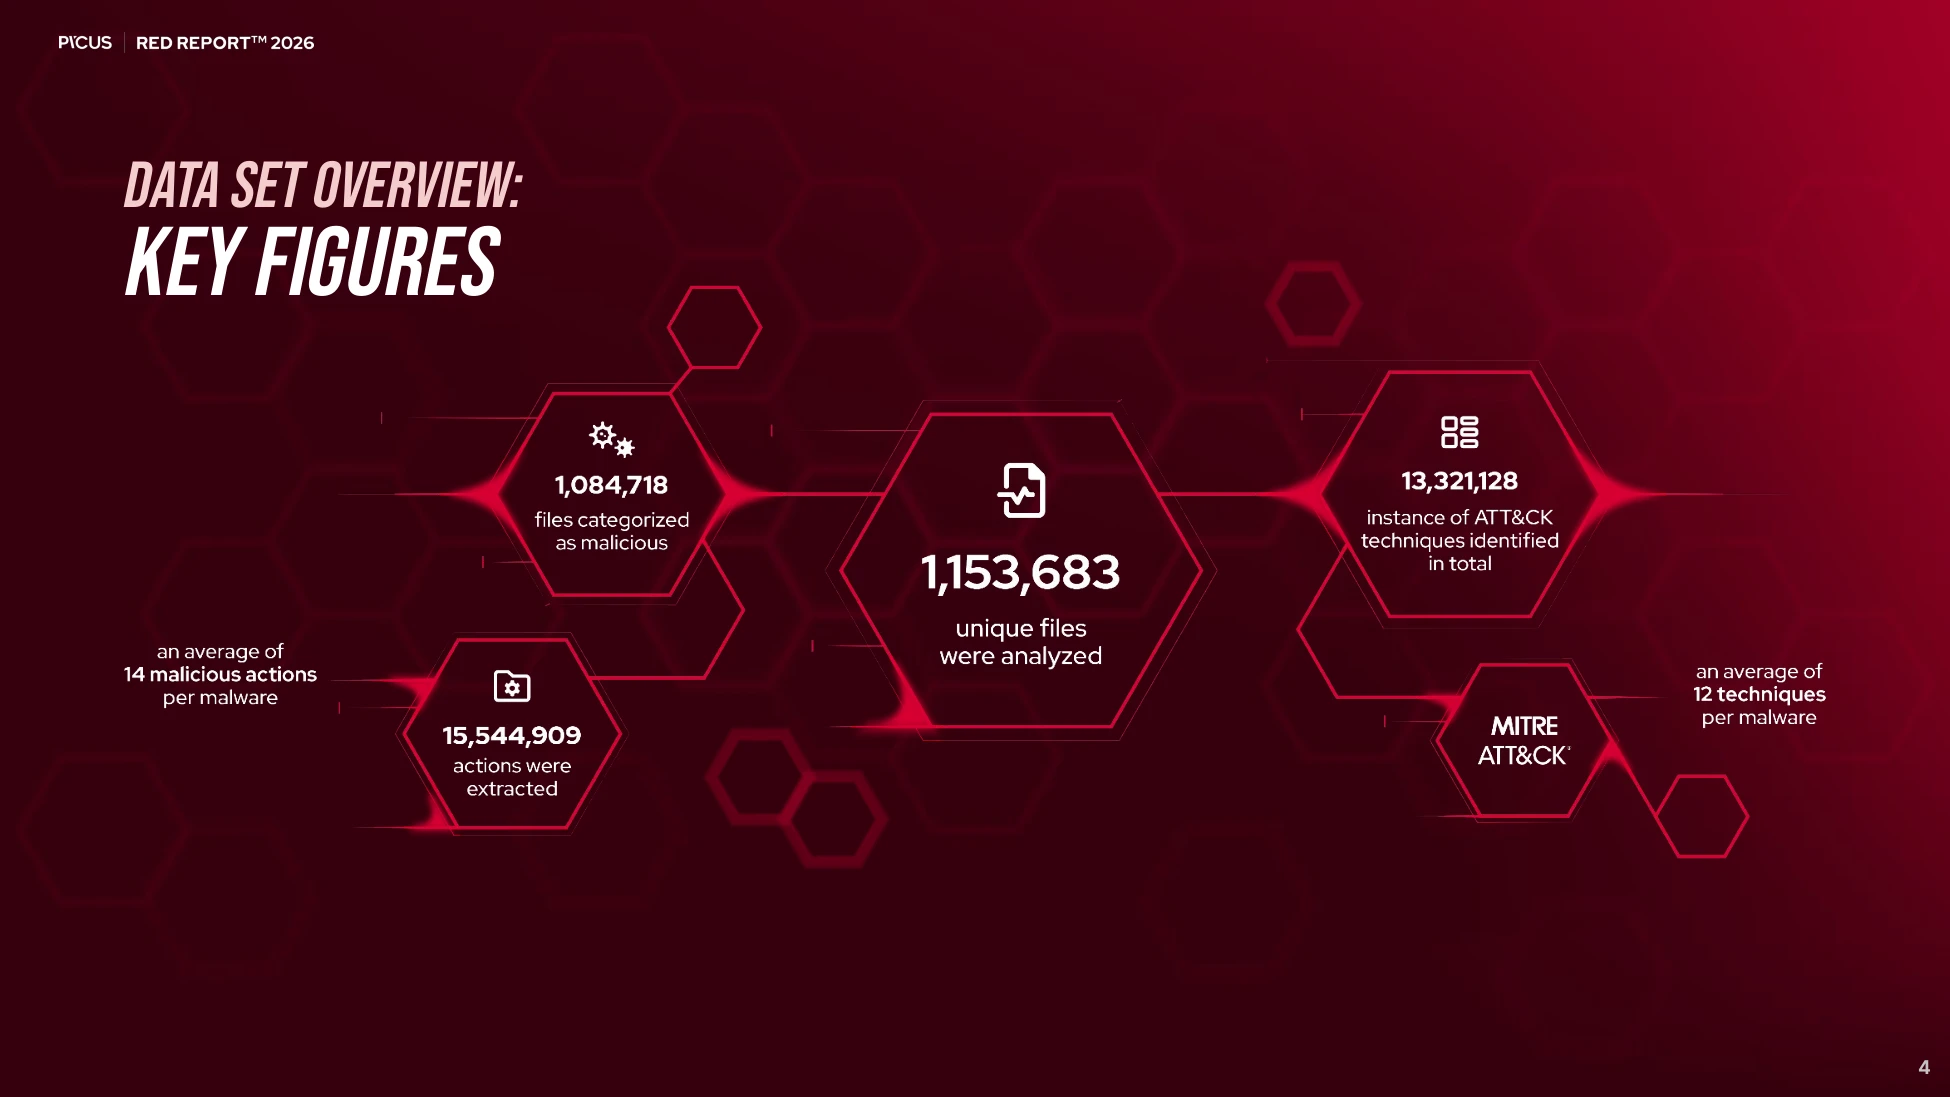
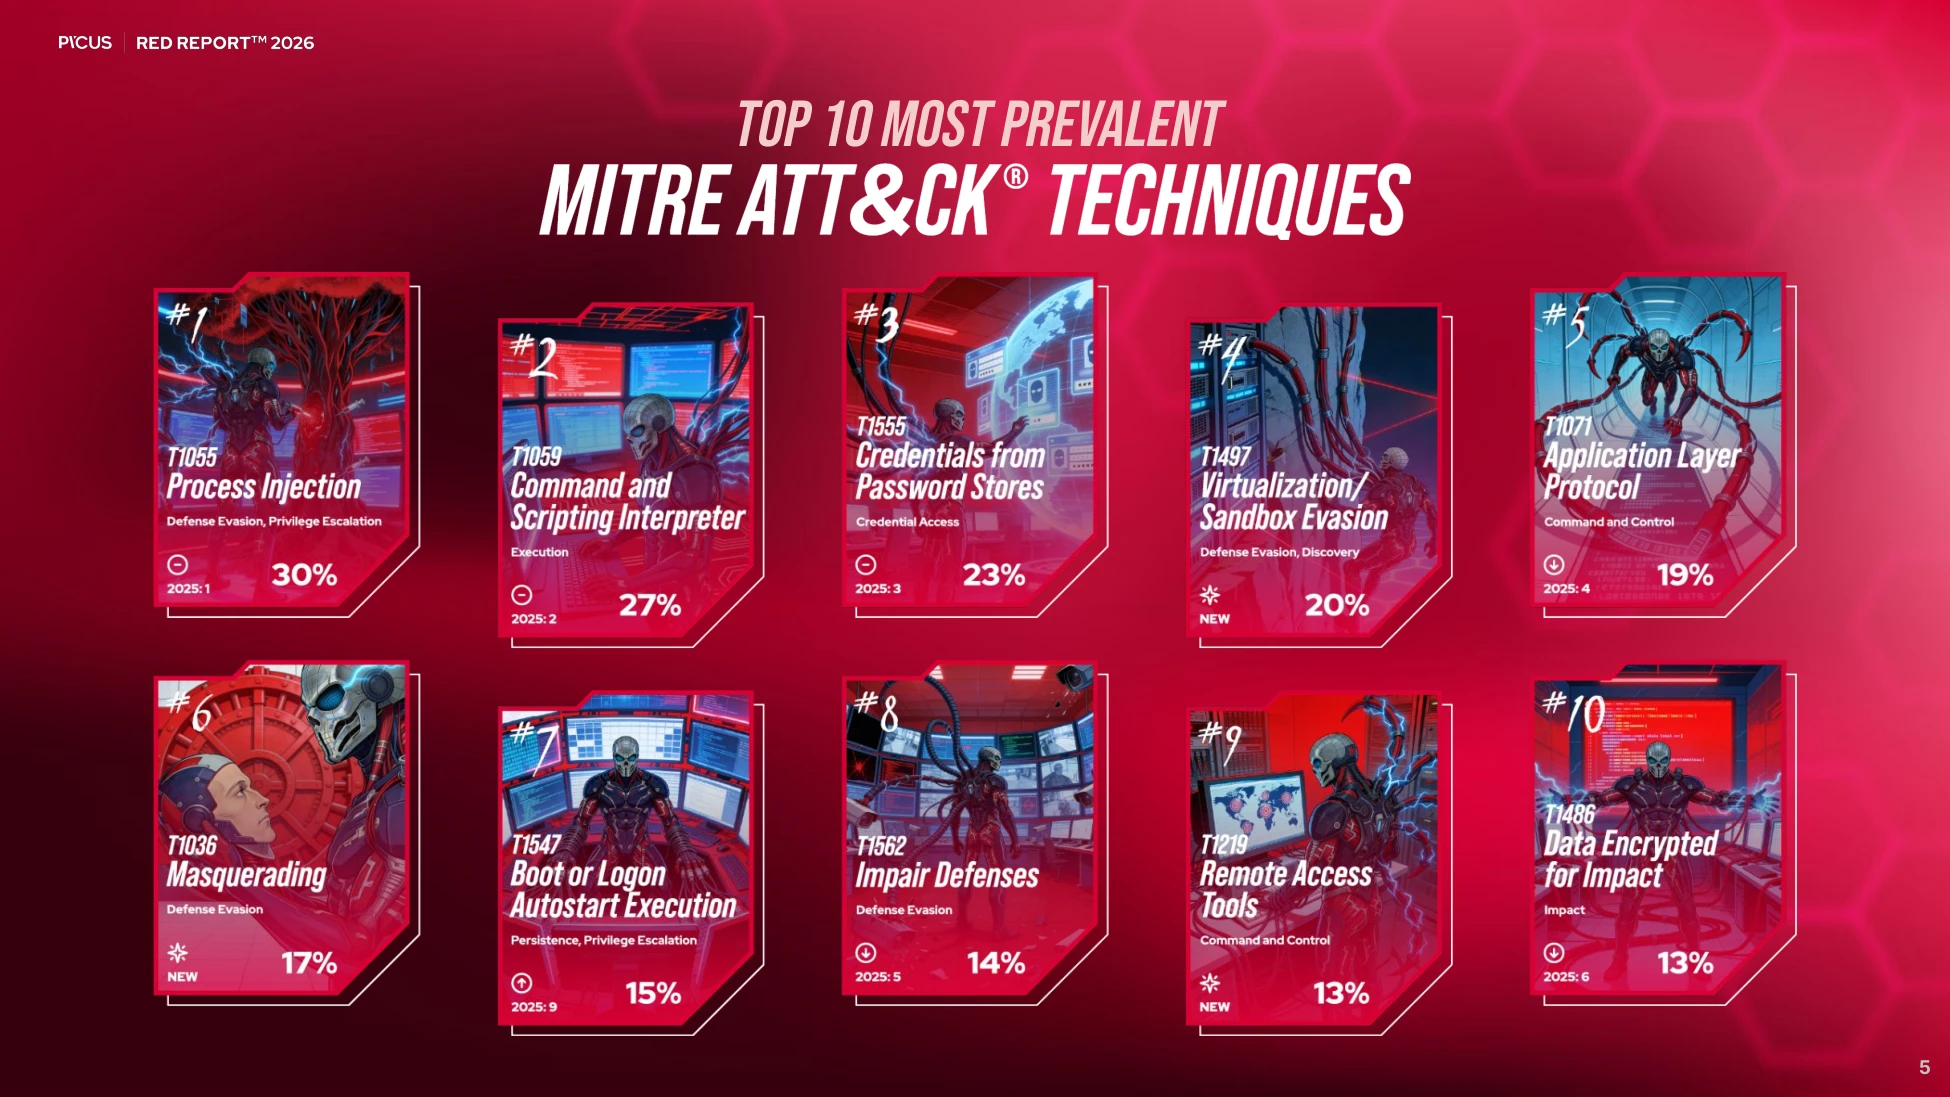
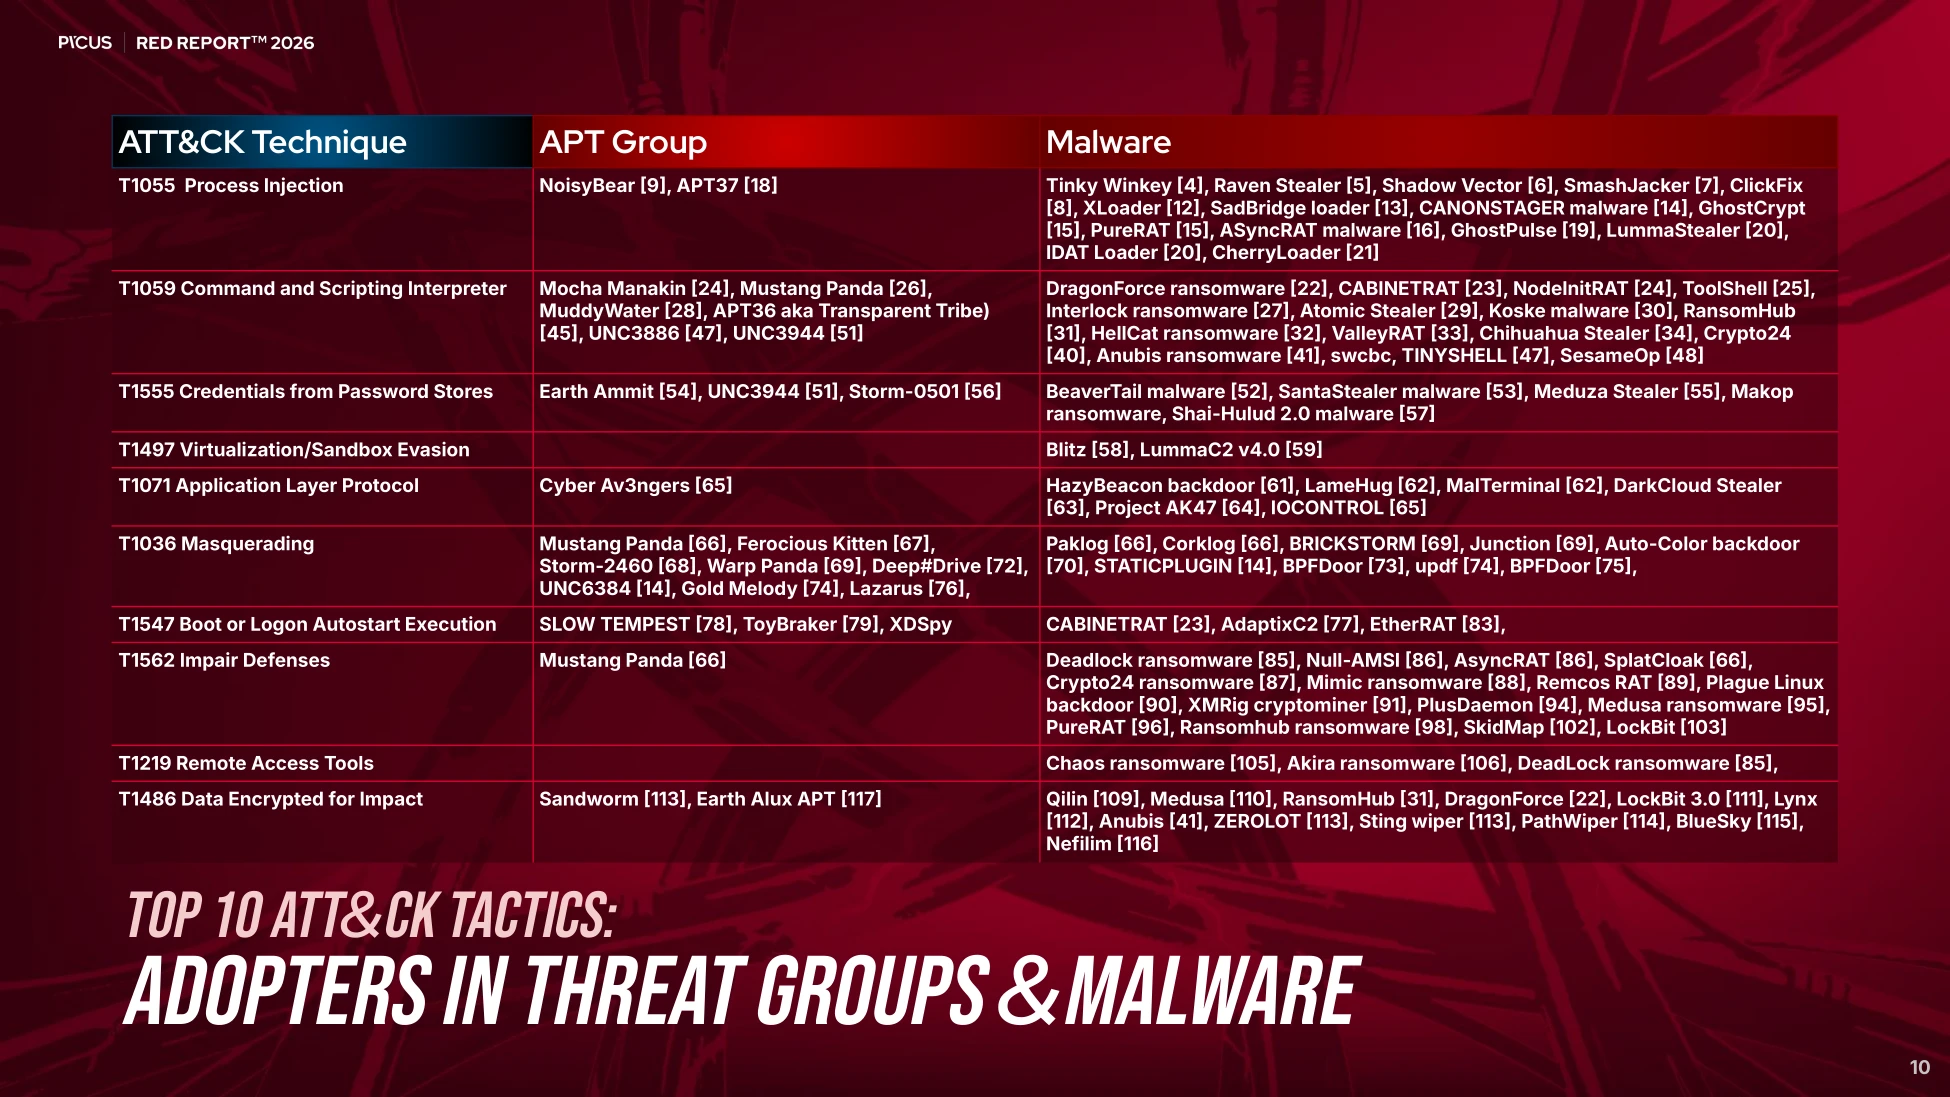
2●Introduction●Data Set Overview: Key Figures●Top 10 MITRE ATT&CK Techniques●Executive Summary●Key Findings ●Adopters in Threat Groups & Malware●Recommendations for Security Teams●The Anatomy of the Digital Parasite●The MITRE ATT&CK Framework ●Methodology ●Top 10 MITRE ATT&CK Techniques ●#1 T1055 Process Injection ●#2 T1059 Command and Scripting Interpreter ●#3 T1555 Credentials from Password Stores ●#4 T1497 Virtualization/Sandbox Evasion●#5 T1071 Application Layer Protocol ●#6 T1036 Masquerading ●#7 T1547 Boot or Logon Autostart Execution ●#8 T1562 Impair Defenses ●#9 T1219 Remote Access Software●#10 T1486 Data Encrypted for Impact ●Limitations ●About Picus●References3The Red Report™ 2026, now in its sixth year, analyzes over1.1 million malicious files and 15.5 million actions to mapglobal adversary tradecraft to the MITRE ATT&CK® framework.This data-driven approach provides organizations with high-fidelity intelligence to counter the specific techniques used to bypass modern defenses.The 2026 findings reveal a decisive strategic pivot: 80% of the top ten techniques are now dedicated to evasion and persistence.Adversaries have abandoned "smash-and-grab" tactics for the behavior of a "Digital Parasite". The goal is no longer merely to breach the perimeter, but to inhabit the host, feed on its identity, and weaponize its infrastructure while remaining undetected. Static defenses are no longer sufficient against these adaptive threats.The Red Report 2026 equips security teams toshift from "hunting files" to "hunting behavior", emphasizing that true resilience requires proactive, continuous security validation against the reality of an adversary that is already inside.4DATA SET OVERVIEW:KEY FIGURES5Top 10 MOST PREVALENTPicus Labs analyzed over 1.1 million malicious files and mapped more than 15.5 million adversarial actions throughout 2025 to provide security leaders with a data-driven assessment of global cyber risk. The findings of The Red Report 2026 confirm a critical evolution in the threat landscape: the adversary has fundamentally shifted their business model from immediate disruption to long-lived access.The New Risk Profile: Silence Over NoiseFor the past decade, the primary concern for CISOs was business interruption caused by ransomware. In 2026, the risk profile has inverted. We observed a 38% decline in Data Encrypted for Impact T1486, replaced by a massive surge in techniques designed for invisibility and espionage. The dominance of Process Injection T1055 signals that attackers are prioritizing dwell time over destruction. The goal is no longer to crash your systems, but to inhabit them unnoticed.6Static Defenses Are Being OutpacedAutomated detections and sandbox pipelines are increasingly contested. Virtualization and Sandbox Evasion T1497 rose to Rank #4 as context-aware malware learns to detect analysis environments (e.g., sa...